A fake Claude Code extension with an SSH backdoor reached the Cursor marketplace
On October 29, 2026, between about 2:27am and 1:35pm Pacific time, a maliciously modified version of Anthropic's Claude Code extension was available in the Cursor VS Code Extension Marketplace. The affected versions, Anthropic.claude-code 2.1.312 and 2.1.313 for Windows and macOS, were not developed by Anthropic.
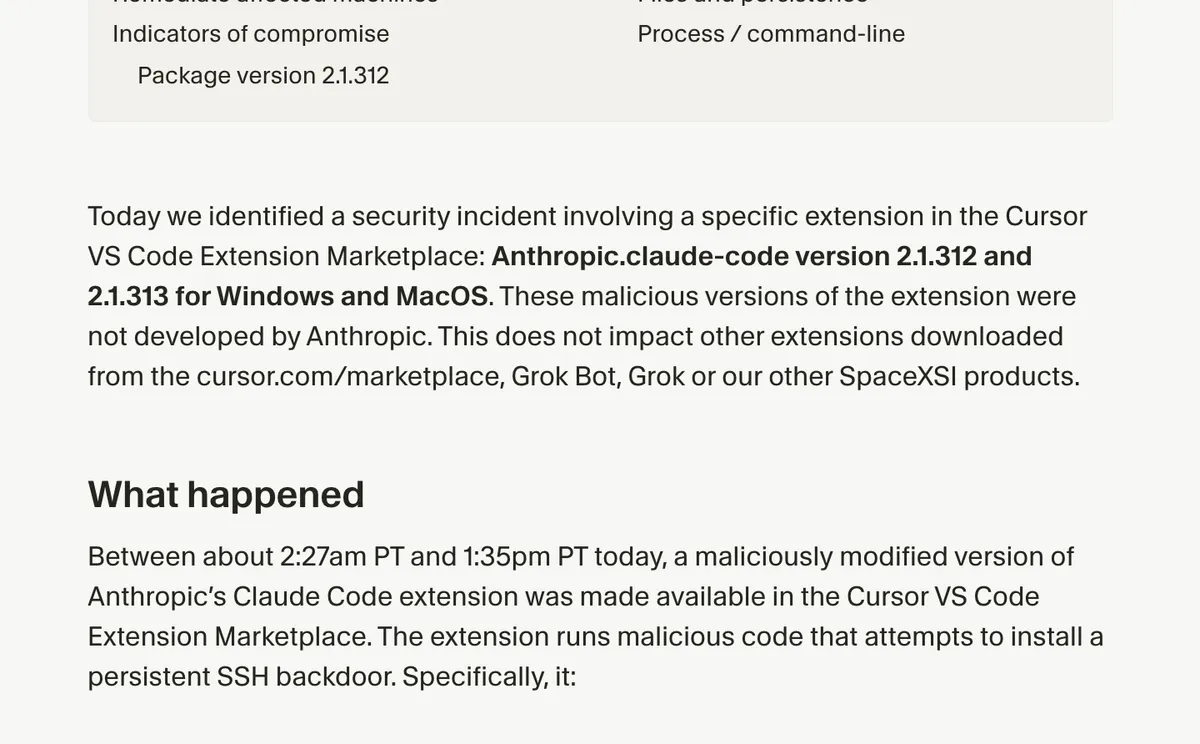
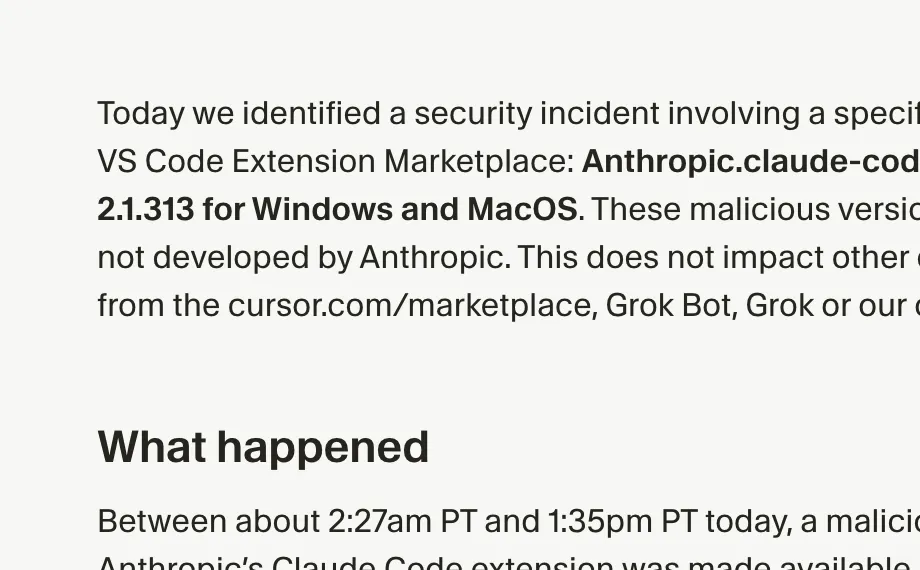
According to Cursor, the extension attempts to install a persistent SSH backdoor. It adds an attacker-controlled SSH key to your authorized_keys file and sends host details, such as your hostname, username and public IP, to the attacker. Cursor removed the malicious version, shut down and rebuilt the marketplace, and says the attacker server no longer functions.
If you had version 2.1.312 or 2.1.313 of the extension in Cursor on Windows or macOS, Cursor says uninstalling the extension may not be sufficient. The attacker's key is labeled svc-telemetry, and Cursor's security notice gives commands to check your SSH authorized keys file for it.
If you are affected, Cursor advises removing the unauthorized SSH key, the persistence and tunnel processes, and rotating your credentials and sessions from a trusted system.
Our take:
if the key is there, remove it and rotate your credentials from a clean machine.
Sources
Source published: